Smart-card credentialing by IDFactors

Confidence in every credential starts here.

Issue. Verify. Manage.

Issue, check and manage smart-card credentials through a clear Windows workflow. Authara brings your TrustPoint Desktop Reader, certificate workflows and credential records together, so your team can focus on the people who depend on them.

  • Local deployment
  • Hardware-backed workflows
  • Role-based controls
Authara dashboard: card registry chart, the TrustPoint Desktop Reader found and the signing CA YubiKey found

The challenge

Strong security starts with a trusted credential.

For many organizations the card itself is the weak point: a Prox or MIFARE card is just a number with no cryptographic identity, and it can be cloned without the access system ever knowing.

Government agencies

The non-PIV personnel gap

Agencies have established PIV programs for federal employees. The gap is the people around them: contractors, new hires waiting for PIV issuance, temporary staff and recurring visitors. They need access to controlled facilities but don't hold a PIV or CAC card.

Defense contractors

The CMMC infrastructure gap

CMMC Level 2 asks defense contractors to meet the Physical Protection controls in NIST SP 800-171, including audit logs tied to individual identity. Prox and MIFARE cards can't provide that, and a full PKI deployment, often with a PACS replacement, is out of reach for many smaller contractors.

Today's options, and where they fall short

Current approachThe resulting problem
Issue a Prox or MIFARE cardNo cryptographic identity. Card numbers can be cloned, and the audit log records a number, not a verified person.
Wait for full PIV issuancePIV issuance for contractors can take weeks or months. Blocking access in the meantime is impractical.
Join the Federal PKI BridgeEnrolling in a federal trust chain is complex and expensive.

Authara closes the gap. Issue PIV-compatible TrustPoint Cards from your own domain, own the key pair, and keep the access control system you already have.

How it works

A clear path to issuing credentials.

Issue with a guided process.

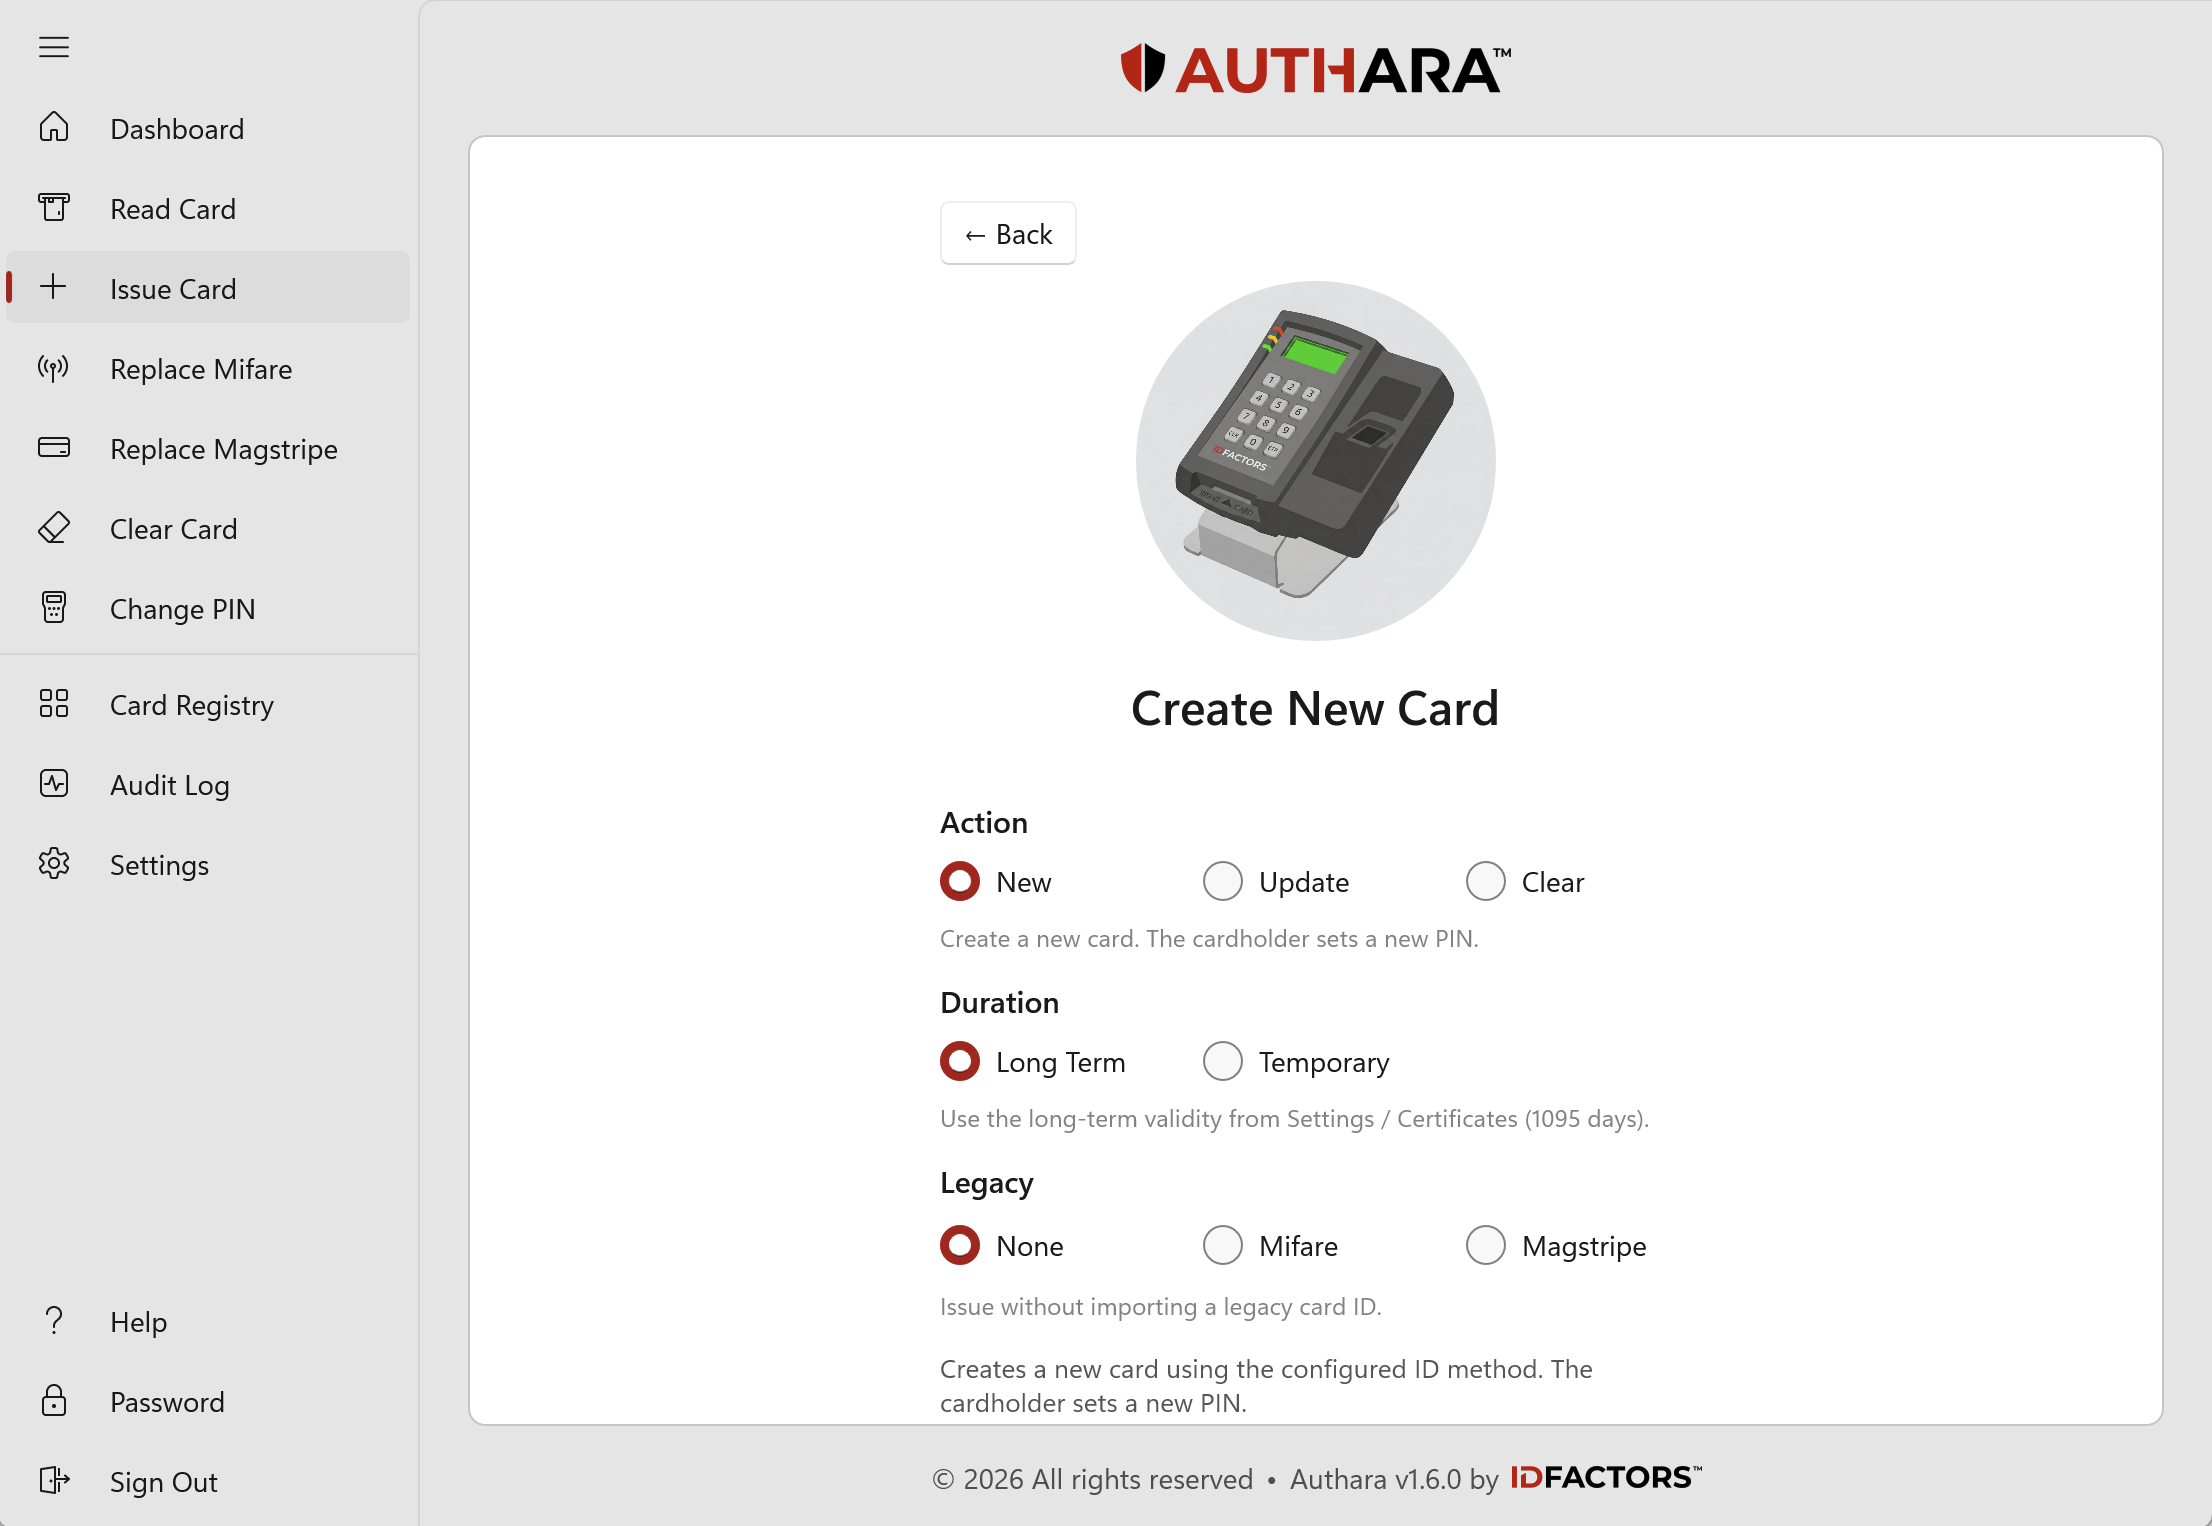
Create and personalize PIV-compatible TrustPoint Cards. Authara coordinates on-card key generation, certificate signing, identity information and cardholder PIN setup through the TrustPoint Desktop Reader. Temporary credentials are supported when your policy calls for a shorter validity period.

Authara Create New Card screen with action, duration and legacy-card options

Credential lifecycle

From enrollment to the door.

A PIV-compatible credential for secure physical access, with optional Microsoft AD logical access.

Identity & enrollment

  1. End userUser identity & attributes
  2. Microsoft ADUser identity & attributesEnrollment agent YubiKeyOptional
  3. Legacy cardsLegacy IDOptional

Authara credential issuance

  1. Authara softwareIssuance policyLifecycle status & audit
  2. TrustPoint Desktop ReaderCard issuanceCA certificate provisioned
  3. TrustPoint CardGenerates its key pairPrivate key retained on the card
  4. Certificate authorityCA key held on a separate YubiKeySigns the certificate
  5. Certificate issuedWritten to the card
  6. Issued TrustPoint CardCard ready

Access outcomes

  1. TrustPoint Door Reader
    1. Sends a challenge
    2. Card signs it
    3. Verifies signature + certificate
    4. Confirms configured CA trust
    Cryptographically validated identity
  2. PACSApplies permissions
  3. Door / secured areaAccess granted or denied
Optional logical accessPIV sign-in to systems that use Microsoft AD

Current scope Authara manages issuance, certificate status and audit history. Future CMS/PACS integration will propagate credential-status changes.

Security design

Sensitive operations belong in the right place.

Authara coordinates the process. Dedicated hardware performs the sensitive card operations.

PIN entry stays on the reader

Cardholders enter their card PIN on the TrustPoint Desktop Reader's keypad, not on the computer.

Authentication keys stay on the card

Private keys generated on the card are used there, and never exported to the desktop application.

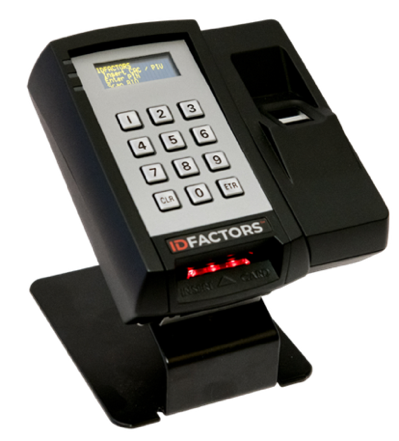
TrustPoint Desktop Reader with display, keypad and fingerprint sensor on its desk stand
TrustPoint Desktop Reader with Hardware Verification Module (HVM)

Signing uses protected hardware

A separate YubiKey holds the CA signing key and signs certificates. The signing key stays on the YubiKey.

Responsibilities are defined

Administrator, Manager and Operator roles control who can use each function.

Built for credentialing at the desk

The TrustPoint Desktop Reader brings card operations, PIN entry and on-reader guidance to the issuance workstation. A separate YubiKey holds the CA signing key and signs certificates.

  • Contact and contactless card operations
  • Keypad for secure PIN entry and PIN change
  • On-reader display guides the officer and cardholder through each step

Deployment

Credentialing where you need it. Records under your control.

Authara runs on a Windows workstation and keeps its operational records locally. An offline installer supports restricted and air-gapped environments, and core credentialing works without a cloud service.

What you need

  • Autharafor Windows
  • TrustPoint Desktop Readerwith Hardware Verification Module (HVM)
  • Separate YubiKeyholds the CA key and signs certificates
  • TrustPoint Cardsmade by Taglio
Authara Settings Overview: officers, organization, card ID format, issuance, signing CA and Microsoft AD
Settings overview: officers, organization, card ID format, issuance, signing CA and Microsoft AD in one place.

Integrations

Connect credentials to your existing environment.

Optional Windows logon with AD CS

Physical-access credential issuance does not require Microsoft AD integration. For optional Windows domain logon, use supported Microsoft Active Directory Certificate Services workflows to prepare smart-card credentials for Windows domain logon, alongside the required enterprise trust, account mapping and policy configuration.

Keep your legacy PACS ID

Credentials can carry the cardholder's legacy PACS ID in the certificate, so your PACS controllers and database stay as they are. Plan and test the migration with your access-control team for the cards and formats at your site.

Information where it's needed

Share selected credential records and events through webhooks, a localhost REST API and CSV exports, for reporting and downstream integration.

Who it's for

Built around the people responsible for credentials.

  • Credentialing operators

    Follow a consistent process for issuance, updates, personalization and PIN workflows.

  • Security managers

    Review credential status, lifecycle history and validation findings.

  • IT and PKI administrators

    Configure certificate workflows, operator permissions and enterprise integration.

  • Integration partners

    Connect selected credential data to reporting and physical-access workflows.

FAQ

Questions about Authara.

What is Authara?

Authara is a Windows desktop application from IDFactors for issuing, reading, updating, personalizing and managing supported smart-card credentials. It works with the TrustPoint Desktop Reader and a configured certificate authority.

Does Authara require a cloud service?

No. Core credentialing doesn't require a cloud service. Authara supports offline installation and keeps its records locally. Features that use enterprise services or external validation evidence need access to those services, or appropriately maintained local evidence.

What hardware does it need?

Card operations need a TrustPoint Desktop Reader and TrustPoint Cards, which are made by Taglio. The reader's Reader Security Module uses a YubiKey as the certificate authority. Any other signing infrastructure depends on your deployment model.

Can Authara support Windows smart-card logon?

Yes. Authara supports certificate workflows for Windows smart-card logon, including Microsoft AD CS integration. Successful logon also depends on your domain configuration, certificate trust, account mapping and revocation infrastructure.

Does a validation pass grant access?

No. A validation result describes the configured checks and the evidence behind them. Authentication establishes the claimed identity; the receiving access system decides what that identity may do. A later check of a stored credential record doesn't prove the card is currently present.

Can Authara work with my existing physical access system?

Authara supports legacy-ID migration and shares data through webhooks, a localhost API and CSV. At the door, TrustPoint Readers verify each card and pass the credential number to your PACS as before. Compatibility needs to be confirmed for the exact credential formats and access system at your site.
Build a clearer credentialing process.

Tell us about your credential types, enrollment needs and integration requirements, and talk with our team about how Authara fits your environment.

Or call 510-545-4393